Forensic Receipts: From Trusted to Proven

Part 6 of the Building the AI Memory Stack series

At the end of the last article, I left one question unanswered.

Can you prove this record is exactly what was written?

Write-Side Custody decides which writes are trustworthy enough to become memory. But a decision to trust something is not the same as being able to prove it later.

Picture that deployment record one more time. Custody examined it, judged it authoritative, and let it become institutional memory. Six months on, an auditor asks a harder question: how do you know it hasn’t changed since?

“We only accept trustworthy writes” is a policy.

It is not proof.

Trust Is a Claim. Proof Is Evidence.

Custody and receipts answer two different questions.

Write-Side Custody asks: should this be trusted?

A Forensic Receipt asks: can this be proven?

The first is a judgment made at the moment of the write. The second is a piece of evidence that outlives the judgment, so that anyone, later, can verify the record for themselves without having to trust the system that stored it.
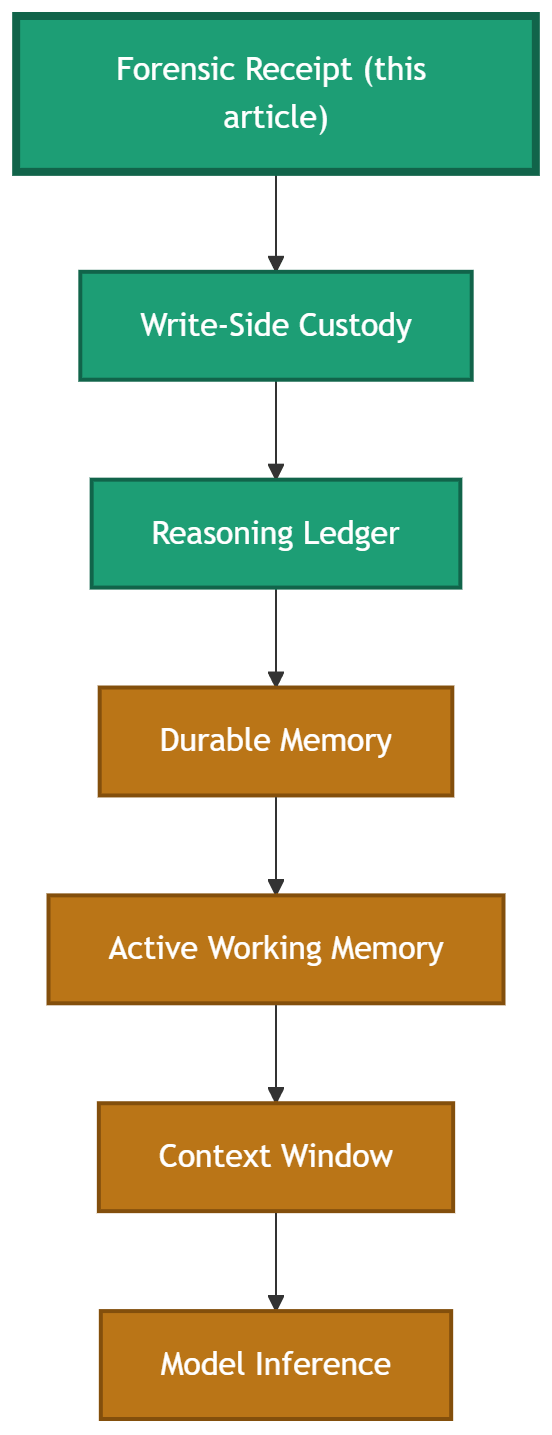
Diagram of the AI memory stack showing Forensic Receipt flowing through Write-Side Custody, Reasoning Ledger, Durable Memory, Active Working Memory, and Context Window to Model Inference. Forensic Receipt is highlighted as the focus of this article.

With that, the stack reaches bedrock. Every layer above now rests on a foundation that can be verified independently.

What a Forensic Receipt Is

The Sovereign Systems Specification calls this evidence a Forensic Receipt.

It is not a log entry. Log entries can be edited, reordered, or quietly rewritten. A Forensic Receipt is a cryptographic fingerprint of a record, captured and signed at the moment the record is written.

Change one character of the record, and the fingerprint no longer matches. The tampering isn’t hidden. It’s mathematically obvious.

In practice, a receipt might look like this:

forensic_receipt:
  record: reasoning_ledger/deploy-2026-03-14
  content_hash: sha256:3af9c1...e07b
  signed_at: 2026-03-14T09:22:07Z
  signature: ed25519:9d4a...c2
  signed_by: sovereign-node-07
  prior_receipt: sha256:8b21...44a

Two fields do most of the work.

The content hash binds the receipt to the exact bytes of the record. Nothing can be altered without breaking it.

The prior receipt links each record to the one before it, forming a chain. You cannot quietly remove or reorder history without every downstream receipt failing.

That is chain of custody, expressed as mathematics rather than as a promise.

Why Logs Aren’t Enough

Most systems already keep audit logs.

The problem is that an audit log is only as trustworthy as whoever controls it. If someone can write to the log, they can usually rewrite it, and a log that can be rewritten proves nothing about the past.

A Forensic Receipt inverts that. It doesn’t ask you to trust the operator, the database, or the backups. Verification depends on cryptography, not on authority, so the evidence speaks for itself.

That distinction is the whole point.

Custody earns trust. Receipts remove the need for it.

The Cost of Proof

None of this is free. Every receipt is a hash computed and a signature generated at write time, which is real work, paid on the write path, exactly where this series has argued trust belongs.

But the alternative is worse. A system that cannot prove its own memory is asking you to take its word for everything it claims to remember.

Proof is the price of being believed later.

The Stack Is Now Trustworthy and Provable

Step back and look at what the six layers guarantee together.

The Context Window executes. Active Working Memory assembles. Durable Memory preserves. The Reasoning Ledger explains. Write-Side Custody decides what to trust. Forensic Receipts prove it.

Execution, assembly, preservation, explanation, integrity, and evidence.

That is a complete architecture for trustworthy institutional memory.

Looking Ahead

We’ve built memory that is durable, explained, trustworthy, and provable.

But it is still sitting in cold storage.

None of it matters until it can return to active reasoning: verified, on demand, and paid for deliberately.

That is where the next article takes us, and where the promise from Part 1 is finally kept. It is the moment memory becomes voice.

Facebooktwitterredditlinkedinmail

Beyond the Hype: Announcing the Open Source Sovereign Systems Specification & Pattern Library

We are currently building AI-native applications inside a linguistic and architectural vacuum.

Over the past year, the industry has thrown billions of dollars at frontier models and cloud orchestration tools while completely neglecting traditional data engineering discipline. We’ve been told that if we simply expand context windows to a million tokens and dump our raw, ambient conversational logs into a managed vector store, the LLM will magically sort it out at runtime.

It doesn’t. Instead, enterprises are hitting massive, systemic walls: attention fragmentation, positional bias (“Lost in the Middle”), data corruption, and skyrocketing API bills.

Recent architectural pivots across the industry—such as multi-agent frameworks shifting away from raw mesh networks to rigid supervisor trees—are symptoms of the exact same underlying disease: we are letting autonomous systems negotiate state through unstructured prose, burning compute without compounding capability.

To break through these walls, we don’t need larger context windows. We need structural boundaries.

Today, I am officially open-sourcing the Sovereign Systems Specification, Glossary, and Pattern Library to establish a rigid, defensive perimeter for local-first AI infrastructure.

Why Patterns Matter: From the Gang of Four to Local Silicon

When the software engineering industry faced the Wild West of early object-oriented development, the “Gang of Four” didn’t invent new languages; they formalized a shared vocabulary in Design Patterns: Elements of Reusable Object-Oriented Software. They gave us names for the invisible structures we were already struggling to build: Singletons, Adapters, Factories. Years later, when the industry shifted from relational tables to document stores, the MongoDB Design Patterns did the same thing for data architecture—formalizing paradigms like the Computed or Outlier patterns so developers could stop guessing how to handle polymorphic, non-relational scaling.

Patterns are essential because the laws of distributed systems do not change just because we throw a neural network in the middle. Right now, AI infrastructure lacks this formalized discipline. Developers are building highly volatile, cloud-dependent “digital attics” because they lack the structural primitives to build load-bearing context pipelines.

The Sovereign Systems Specification bridges this gap, providing repeatable, battle-tested architectural patterns for deterministic, cost-aware, and high-integrity AI inference.

The Sovereign Architecture: Three Pillars of State Control

The core thesis of this resource is simple: We must shift from query-time reasoning to strict write-time ingestion boundaries. We treat incoming payloads as untrusted telemetry on local silicon before an external orchestrator ever touches a cloud model.

This open-source release is split into three distinct, load-bearing resources:

  1. The Sovereign Systems Glossary
    A formalized dictionary designed to give engineering teams a shared vocabulary for data flow, risk, and state control. It moves past prompt-engineering “magic spells” and defines rigid terms like:
    • The Prose Tax & Context Inflation Tax: The geometric compounding of financial cost and model attention decay that occurs when you pass un-optimized, raw text streams across the network.
    • Write-Side Custody: The architectural discipline of enforcing structural validation, cryptographic signing, and metadata parsing at the exact point of ingestion before data ever commits to long-term memory.
    • The Digital Attic (Anti-Pattern): The chaotic enterprise trap of dumping unvetted, unstructured raw logs into vector storage and assuming semantic search can reliably reconstruct operational context at runtime.
  2. The Architecture & Execution Framework (/ARCHITECTURE)
    Comprehensive visual blueprints, execution pipeline flows, and runtime orchestration layouts. These documents map the exact physical transition from cloud-dependent, API-mediated routing to localized, edge-native context processing—ensuring data custody and reasoning models remain entirely unified within a secure local boundary.

  3. The Sovereign Inference Pattern Library (/PATTERNS)
    Repeatable, low-level structural primitives for context engineering. It includes detailed layouts for patterns like the Sieve-and-Sign Pattern (aggressively filtering input for semantic noise locally and stamping it with a cryptographic signature) and Pre-Paid Retrieval Precision (paying a fixed token cost upfront to structure context, eliminating the compounding cost of positional bias during runtime queries).

Accessing the Resources

The entire specification index, architectural layouts, and pattern files are open, human-readable, and live today on GitHub Pages:

How to Contribute

This is a living framework built for practitioners who are actively wrestling with these constraints in production. We are explicitly looking for community contributions to expand this shared language:

  • Pattern Submissions: Have you engineered a repeatable runtime or filtering primitive that successfully prevents boundary deflection or context inflation? Submit an architectural RFC.
  • Case Studies & Anti-Patterns: If your team has successfully migrated away from an ambient context loop or survived a “digital attic” metadata collapse, your post-mortem belongs in this index.
  • Documentation Refinements: Help us sharpen definitions, expand the visual data flow blueprints, or map these patterns to specific local Small Language Model (SLM) topologies.

Check out the specification repo, star the project, and open an issue or pull request to get involved:

Sovereign Systems Specification on GitHub

Let’s stop building fragile cloud wrappers. Let’s start engineering sovereign systems.

Facebooktwitterredditlinkedinmail